01
Discover
Dynamically discover listeners, processes, web services, certificates, and PKI assets. Bring certificate information into PKI Trust Manager to establish visibility across the environment.
Host · process · listener · certificate
Boltron-AI brings intelligence and operational automation into Securetron PKI Trust Manager. It discovers PKI assets, understands context, plans workflows, executes approved runbooks where supported, validates results, and keeps monitoring.
Not a generic chatbot. An operational intelligence layer designed for certificate and PKI management.
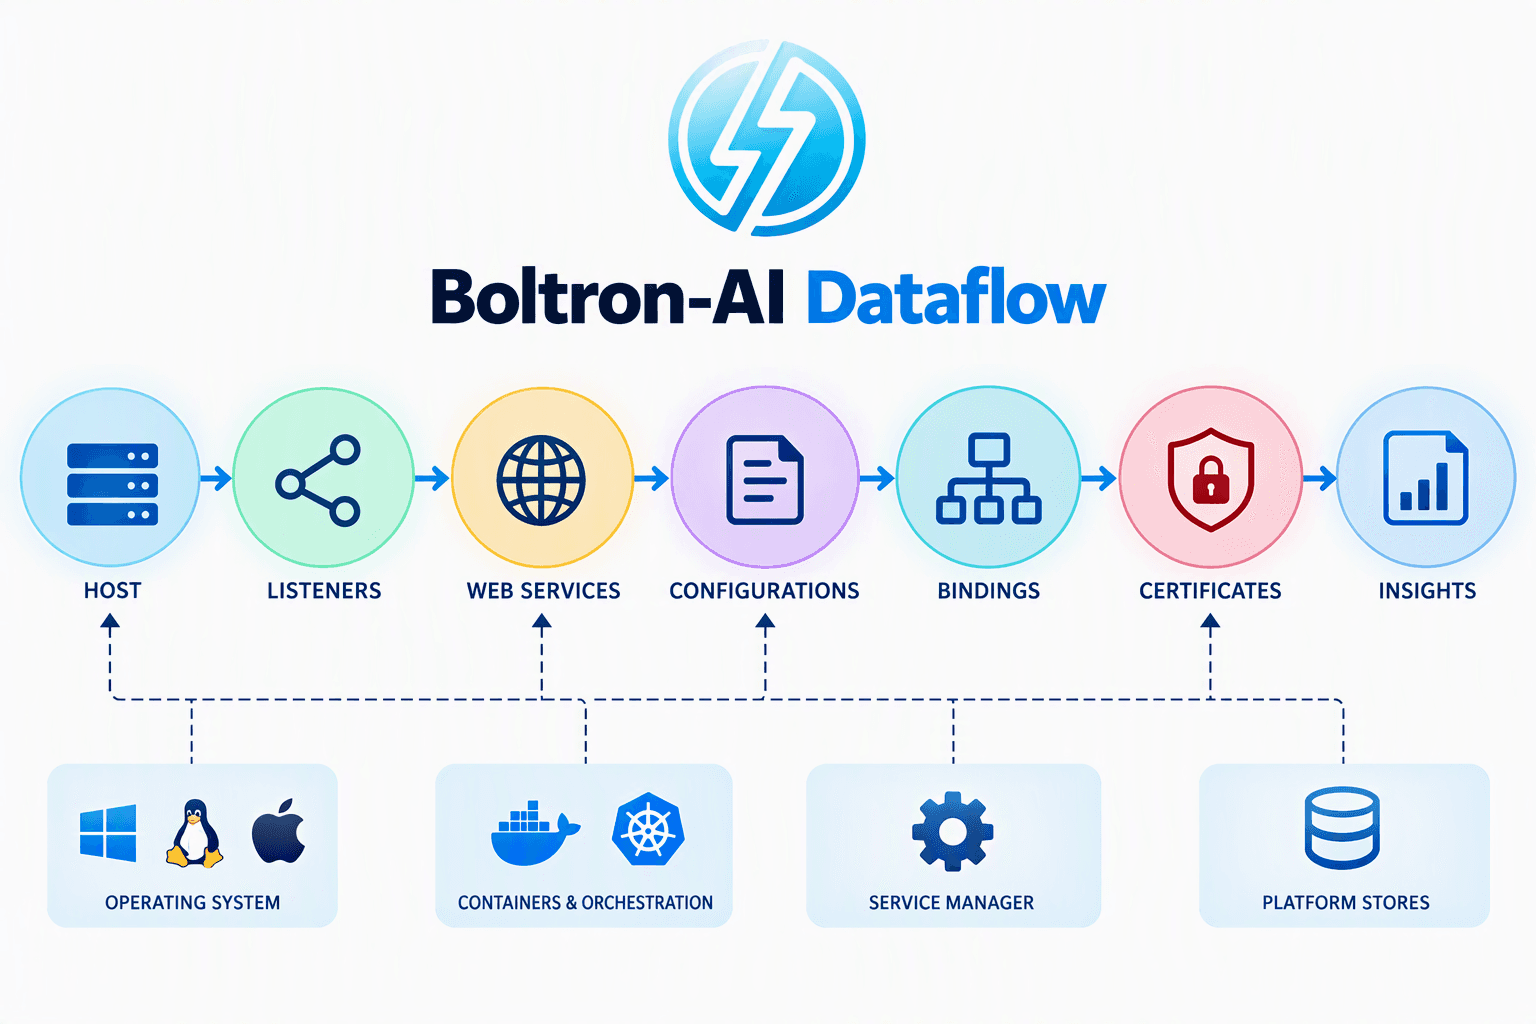
Boltron-AI intelligence and workflow layer for PKI Trust Manager
Enterprise PKI operations span asset discovery, application onboarding, certificate lifecycle tasks, troubleshooting, and repeatable procedures. Boltron-AI adds an intelligence layer inside PKI Trust Manager to help teams move from observed evidence to a planned, reviewable workflow—and, where supported, an approved operational runbook.
Boltron-AI doesn’t stop at telling an administrator what to do. It is designed to carry PKI intelligence into operational automation—executing approved runbooks where the PKI Trust Manager integration supports it.
Dynamically discover listeners, processes, web services, certificates, and PKI assets. Bring certificate information into PKI Trust Manager to establish visibility across the environment.
Host · process · listener · certificate
Analyze the PKI context around a certificate or operational task. Identify what needs attention and the evidence needed to select an appropriate workflow.
Configuration · binding · SNI · upstream
Determine the appropriate operational workflow, select or build on an existing runbook, and identify the actions required to complete the PKI task.
Runbook · steps · confidence · approval
Where supported, execute approved workflows and runbooks to automate repeatable PKI operational activities and reduce manual administrator steps.
Approved actions · bounded execution
Verify the outcome of the workflow. Compare configured certificate references with live TLS evidence and surface mismatches or issues that need administrator attention.
Live TLS · fingerprint · result
Continue monitoring certificates and PKI assets through PKI Trust Manager, identifying conditions that may call for another operational workflow.
Continuous visibility · next action
A practical operational workflow grounded in discovered infrastructure, configuration evidence, and PKI Trust Manager context.
Discover active listeners, owning processes, web services, configuration sources, certificate references, and live TLS endpoints using evidence from the environment.
Correlate processes, services, configuration, bindings, certificates, and applications—recording evidence, confidence, limitations, and unresolved relationships.
Turn discovered context into an appropriate, repeatable PKI workflow. Select an existing runbook or build on one, with the actions and evidence made clear.
Execute approved runbooks where supported by PKI Trust Manager. Read-only discovery stays read-only; changes are bounded to the authorized workflow.
Verify the requested operation completed. Where relevant, compare the certificate configured in a service with the certificate observed through a live TLS handshake.
Continue monitoring through PKI Trust Manager so newly discovered conditions can feed the next operational cycle—not just a one-time AI interaction.
Boltron-AI’s discovery model starts with host identity, listeners, owning processes, configuration sources, bindings, and certificate evidence. Relationships carry evidence and confidence; unresolved links and conflicts stay visible instead of being presented as facts.
The discovery agent is specified as read-only: no service restarts or reloads, no configuration changes, no certificate enrollment or revocation, and no private-key or secret retrieval. Execution is limited to approved runbooks where supported by PKI Trust Manager.
Boltron-AI helps reduce repetitive administration, streamline operational workflows, improve consistency with runbooks, and bring practical intelligence into PKI Trust Manager.